To fix PHP2Shell on Debian, install php8.2 version 8.2.35-1~deb12u1 on Debian 12 bookworm or php8.4 version 8.4.27-1~deb13u1 on Debian 13 trixie from the Debian security archive, then restart PHP.
Both packages shipped on 21 October 2026 and fix CVE-2026-109618 and CVE-2026-109619. This page covers only the Debian 12 and 13 packages; the PHP guide hub collects every other PHP2Shell update, download and mitigation post.
How to install the PHP2Shell fix on Debian with apt
The same four commands work on Debian 12 and Debian 13, as long as the security suite is in your APT sources. Run them as root or with sudo.
- Refresh the package lists with
sudo apt-get update. - Install the pending upgrades with
sudo apt upgrade. On Debian 12 this pulls php8.2 8.2.35-1~deb12u1; on Debian 13 it pulls php8.4 8.4.27-1~deb13u1. - Answer any configuration file prompts carefully, keeping your own php.ini edits unless you know the new file is wanted.
- Restart the PHP service that serves your sites: PHP-FPM, or Apache if you run mod_php.
- Confirm the new version with
dpkg -l 'php8*'(details in the version check section below).
The generic walkthrough for both distributions, including PPAs and unattended-upgrades, lives in the Ubuntu and Debian PHP update guide. This page stays on the exact Debian package versions.
Is Debian affected by PHP2Shell?
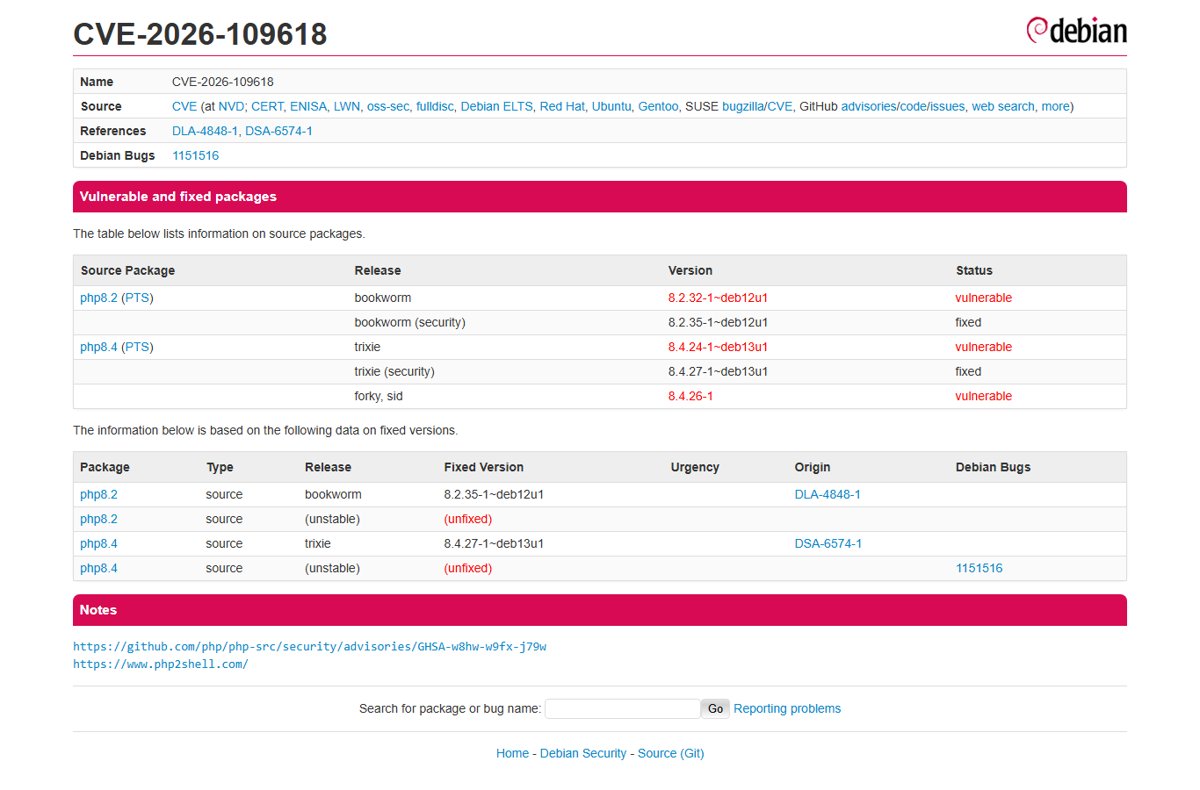
Yes. Every Debian release that ships a PHP package built before the fix is vulnerable, according to the Debian security tracker entries for both CVEs. The table shows the state on 22 October 2026.
| Debian release | Source package | Vulnerable version | Fixed version | Notice |
|---|---|---|---|---|
| Debian 12 bookworm | php8.2 | 8.2.32-1~deb12u1 | 8.2.35-1~deb12u1 (bookworm-security) | DLA-4848-1 |
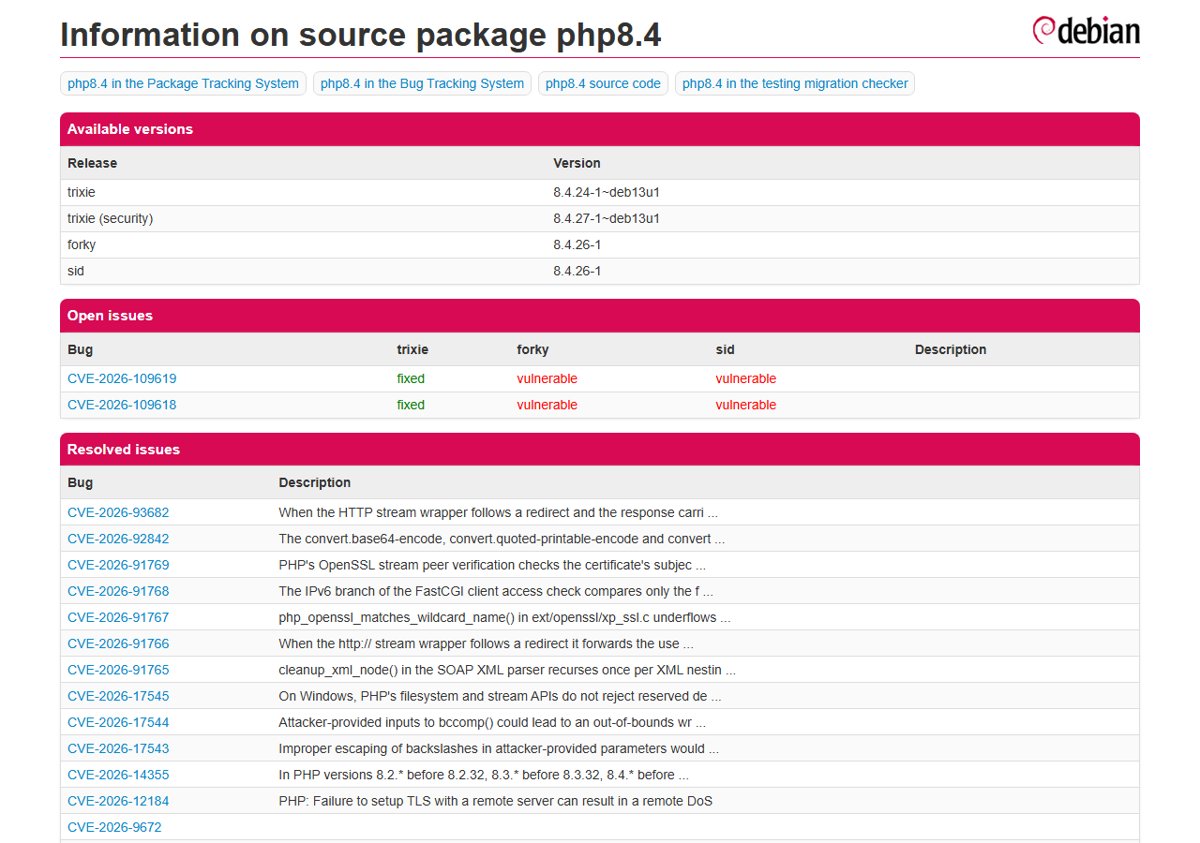
| Debian 13 trixie | php8.4 | 8.4.24-1~deb13u1 | 8.4.27-1~deb13u1 (trixie-security) | DSA-6574-1 |
| Debian forky (testing) and sid (unstable) | php8.4 | 8.4.26-1 | Not fixed yet | Debian bug 1151516 |
PHP.net says all PHP installations serving web requests are at risk, including PHP-FPM, Apache with mod_php and php-cgi. The PHP2Shell patch overview explains both flaws in depth.
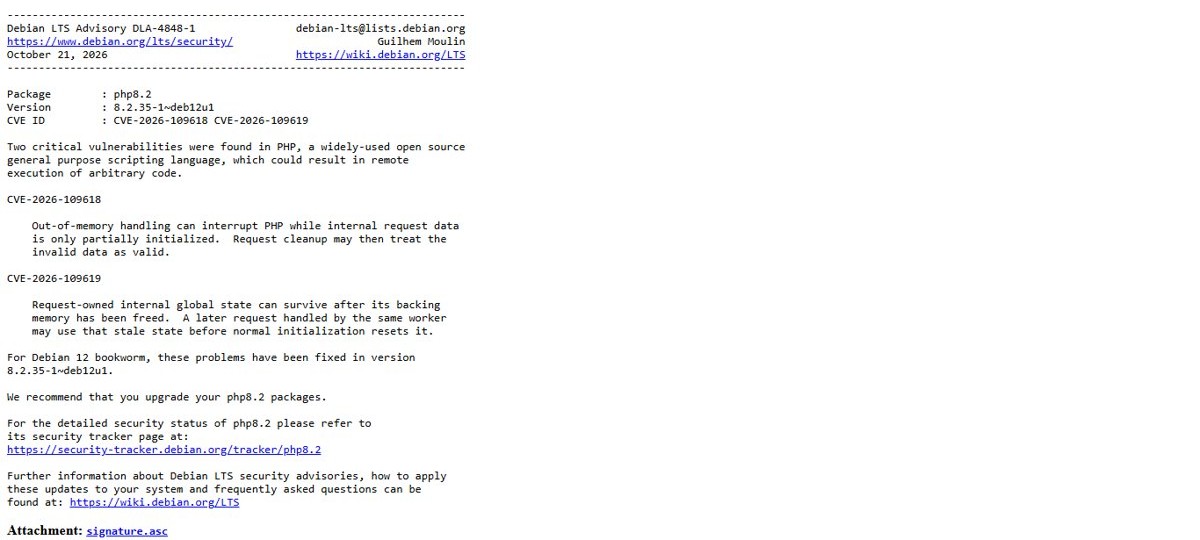
PHP2Shell fixed versions for Debian 12 bookworm (DLA-4848-1)
Debian LTS published DLA-4848-1 for php8.2 on 21 October 2026. It fixes both CVEs in the bookworm package and matches upstream PHP 8.2.35.
| Item | Debian 12 value |
|---|---|
| Advisory | DLA-4848-1 (Debian LTS) |
| Source package | php8.2 |
| Fixed version | 8.2.35-1~deb12u1 |
| CVE-2026-109618 | Out-of-memory handling can interrupt PHP while request data is only partly initialized, and cleanup treats it as valid |
| CVE-2026-109619 | Request-owned global state can survive after its memory is freed and be used by a later request on the same worker |
| Status page | security-tracker.debian.org/tracker/php8.2 |
PHP2Shell fixed versions for Debian 13 trixie (DSA-6574-1)
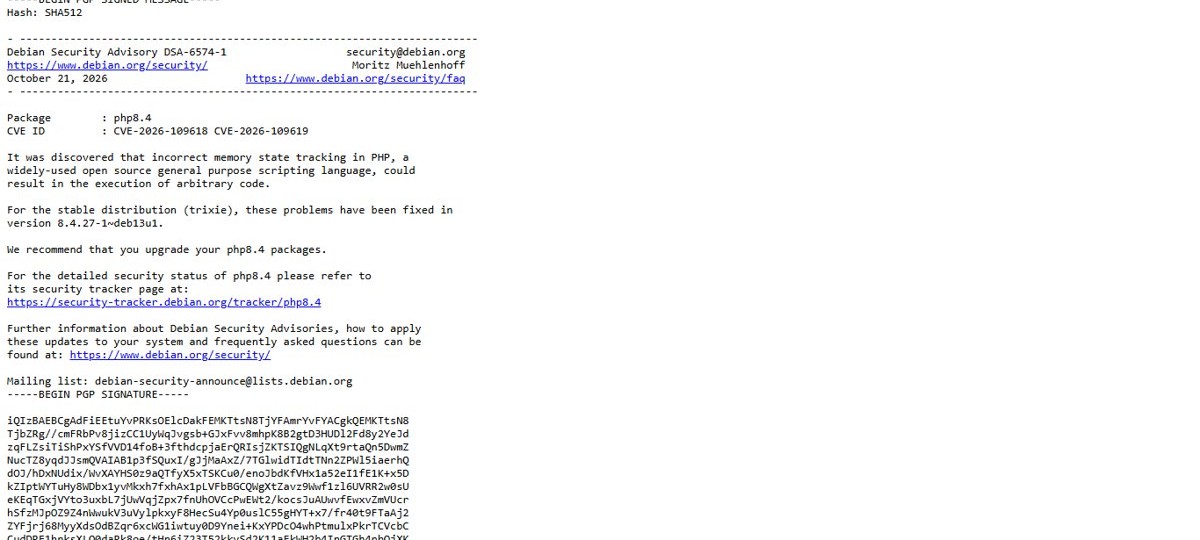
The Debian Security Team published DSA-6574-1 for php8.4 in the stable distribution on 21 October 2026. It describes the issue as incorrect memory state tracking that could result in arbitrary code execution.
| Item | Debian 13 value |
|---|---|
| Advisory | DSA-6574-1 (Debian Security Team) |
| Source package | php8.4 |
| Fixed version | 8.4.27-1~deb13u1 |
| CVEs | CVE-2026-109618, CVE-2026-109619 |
| Upstream equivalent | PHP 8.4.27 |
| Status page | security-tracker.debian.org/tracker/php8.4 |
The Windows builds and the full upstream changelog for this branch are on the PHP 8.4.27 download page. Debian users should take the package above, not an upstream tarball.
Debian 12 LTS security repository for PHP 8.2
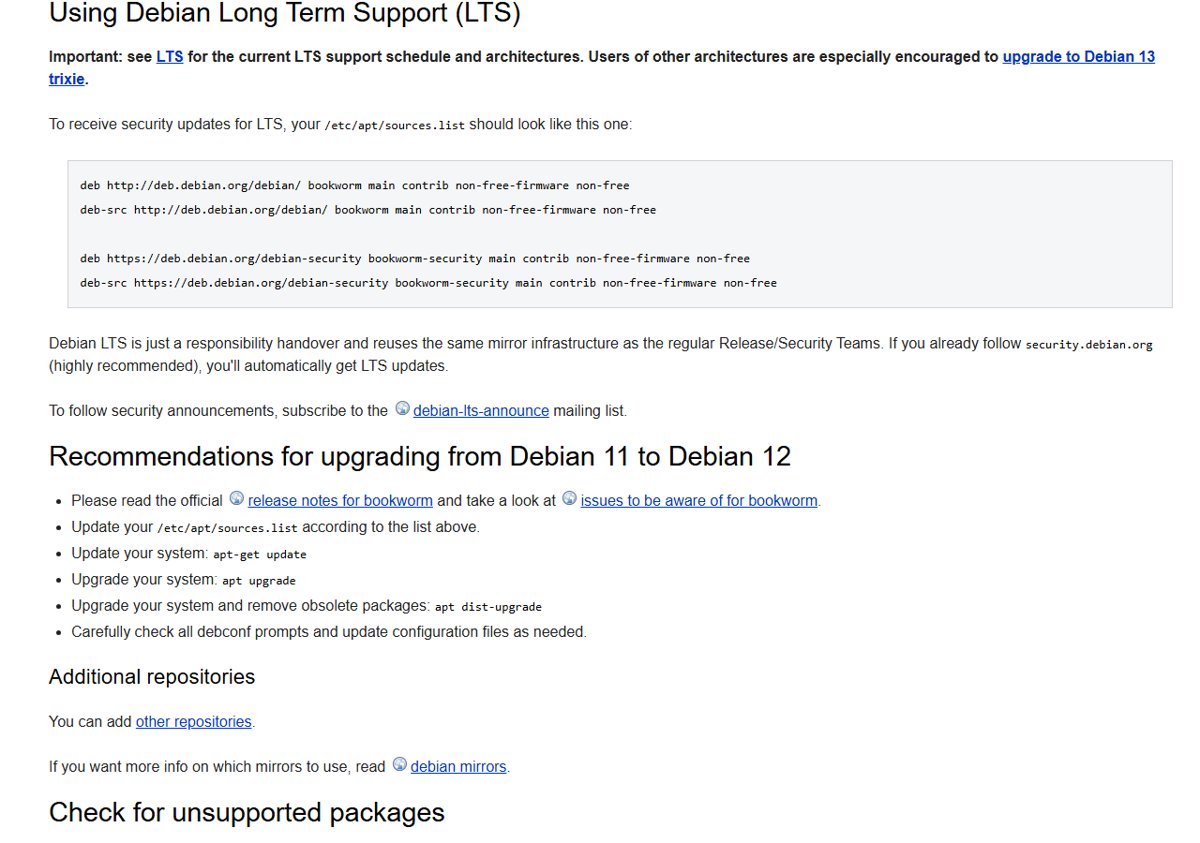
Debian 12 bookworm security updates now come from Debian LTS. LTS reuses the normal security mirrors, so a system that already follows the security archive gets DLA-4848-1 without changes.
The Debian wiki gives this /etc/apt/sources.list for bookworm LTS:
deb http://deb.debian.org/debian/ bookworm main contrib non-free-firmware non-free
deb-src http://deb.debian.org/debian/ bookworm main contrib non-free-firmware non-free

deb https://deb.debian.org/debian-security bookworm-security main contrib non-free-firmware non-free
deb-src https://deb.debian.org/debian-security bookworm-security main contrib non-free-firmware non-free
The bookworm-security lines are the ones that deliver php8.2 8.2.35-1~deb12u1. Drop components you do not use, but keep the debian-security line.
You should see: sudo apt-get update lists a bookworm-security source among the fetched repositories.
On Debian 13, check that your sources include the trixie security suite, because the tracker lists the fix only under trixie (security). To spot packages LTS no longer supports, the wiki recommends the debian-security-support package and its check-support-status tool.
How to check the PHP package version on Debian
Compare the installed package version, not just the PHP version string, against the Debian notice.
dpkg -l 'php8*'Lists every installed php8.x package with its Debian version in the Version column.
You should see: Debian 12 shows 8.2.35-1~deb12u1 for the php8.2 packages; Debian 13 shows 8.4.27-1~deb13u1 for the php8.4 packages.
Then confirm the running interpreter picked up the update: php -v should report 8.2.35 or 8.4.27. For the web side, the PHP version check shows how to read phpinfo safely.
Restart PHP-FPM or Apache on Debian after the php8.2 or php8.4 update
Old worker processes keep the vulnerable code in memory until they restart. CVE-2026-109619 abuses state left behind in a worker, so a restart is part of the fix.
- Find the PHP service with
systemctl list-units 'php*'. - Restart the PHP-FPM unit it lists with
sudo systemctl restart <unit name>. - If Apache runs PHP through mod_php, restart it with
sudo systemctl restart apache2. - Check the unit is active again with
systemctl status <unit name>.
Reload versus restart, and fixes for units that fail to come back, are in the PHP-FPM restart guide.
PHP2Shell on Debian testing and unstable
Debian forky (testing) and sid (unstable) are not covered by DSA or DLA notices. On 22 October 2026 the tracker still marked php8.4 8.4.26-1 there as vulnerable, with the fix tracked in Debian bug 1151516.
On forky or sid, run sudo apt-get update and sudo apt upgrade daily and watch the php8.4 tracker page until it shows a fixed version. No patched forky or sid package exists yet, so the only protection meanwhile is the partial mitigation list from php.net. Those steps are in the PHP2Shell mitigations guide.
Debian PHP2Shell update problems and fixes
apt upgrade does not offer a new php8.2 or php8.4
The security suite is missing from APT sources, so only the older point-release package is visible.
- Add the bookworm-security line from the Debian 12 section, or the trixie security suite on Debian 13.
- Run
sudo apt-get updateagain. - Run
sudo apt upgradeand check the php packages are listed.
dpkg shows the fixed version but php -v still reports the old release
A different PHP binary is first in PATH, such as a copy built from source or from another repository.
- Run
which phpto see the binary in use. - Run
dpkg -Son that path; if no Debian package owns it, it is not covered by the Debian notices. - Update or remove that separate build.
Website still shows the old PHP version after the update
PHP-FPM or Apache was not restarted, so workers still run the old code.
- Restart the PHP-FPM unit or apache2 as shown above.
- Reload the phpinfo page and confirm 8.2.35 or 8.4.27.
Debian 11 or another release has no PHP2Shell notice
The tracker lists fixes only for bookworm and trixie.
- Check the CVE pages on security-tracker.debian.org for your release.
- If no fix is listed, plan an upgrade to Debian 13 trixie, which the Debian wiki recommends.
PHP2Shell on Debian FAQ
What is DSA-6574-1?
DSA-6574-1 is the Debian Security Advisory for php8.4 published on 21 October 2026. It fixes CVE-2026-109618 and CVE-2026-109619 in Debian 13 trixie with version 8.4.27-1~deb13u1.
What is DLA-4848-1?
DLA-4848-1 is the Debian LTS Advisory for php8.2, published on 21 October 2026. It fixes both PHP2Shell CVEs in Debian 12 bookworm with version 8.2.35-1~deb12u1.
Which Debian 12 PHP 8.2 security update fixes PHP2Shell?
php8.2 version 8.2.35-1~deb12u1 from bookworm-security fixes it. Earlier bookworm builds, including 8.2.32-1~deb12u1, are listed as vulnerable by the Debian security tracker.
Which Debian 13 PHP 8.4 version fixes CVE-2026-109618?
php8.4 version 8.4.27-1~deb13u1 fixes CVE-2026-109618 and CVE-2026-109619 on Debian 13 trixie. The older 8.4.24-1~deb13u1 package in the main trixie suite is still vulnerable.
Do I need to add a new repository for Debian 12 LTS?
No, if you already use the Debian security archive. Debian LTS reuses the regular security mirrors, so the bookworm-security line delivers DLA-4848-1 automatically.
Is PHP2Shell fixed in Debian testing or sid?
Not yet. On 22 October 2026 the Debian security tracker still listed php8.4 8.4.26-1 in forky and sid as vulnerable, tracked in Debian bug 1151516.
Can unattended-upgrades install the Debian PHP2Shell fix?
Yes. Debian recommends the unattended-upgrades package to keep a system current with security updates automatically. You still need to restart PHP-FPM or Apache afterwards so workers load the patched code.
Bottom line: patch Debian PHP2Shell today
Run apt upgrade from the security suite, confirm 8.2.35-1~deb12u1 or 8.4.27-1~deb13u1 with dpkg, then restart PHP-FPM or Apache. Both fixed Debian packages are out, PHP2Shell allows unauthenticated remote code execution, and the fix is not active until the PHP workers restart.